

Device
Inside Armv9 Memory Tagging Extension: Hardware Architecture, Pointer Tags, and Android Kernel Hardening
An exhaustive systems engineering analysis of Armv9 Memory Tagging Extension (MTE): exploring 4-bit physical memory tags, Top-Byte-Ignore (TBI) pointer coloring, Synchronous vs. Asynchronous CPU trap modes, Scudo memory allocator internals, and Linux/Android kernel heap exploitation mitigations.
12 min read
Inside Armv9 Memory Tagging Extension: Hardware Architecture, Pointer Tags, and Android Kernel Hardening
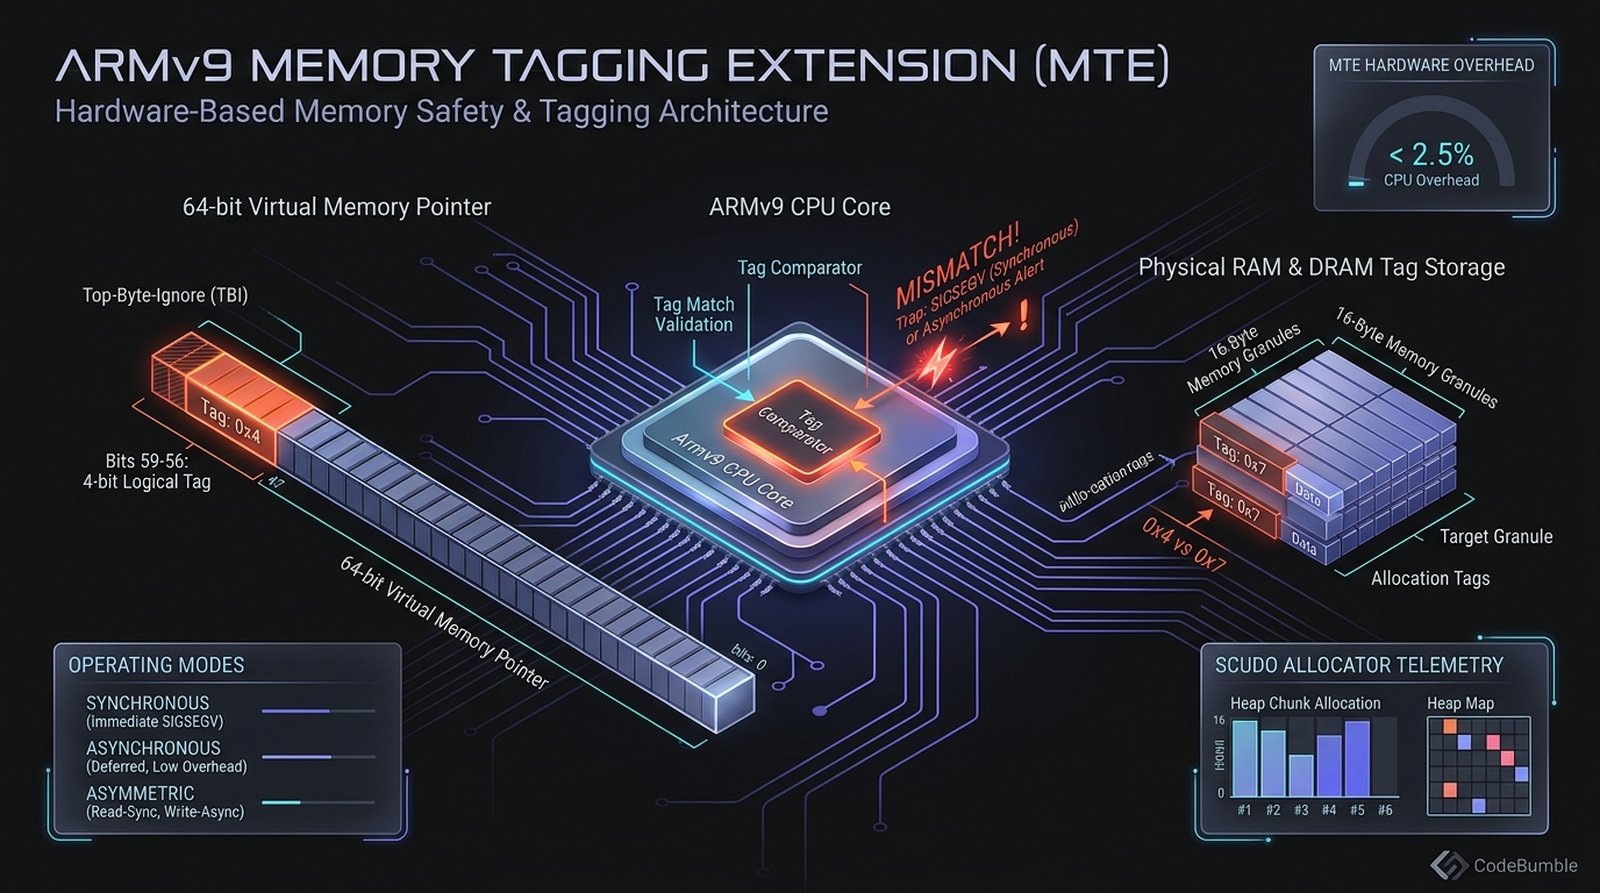
For five decades, systems engineering and systems software development in C and C++ have operated under the persistent shadow of memory safety vulnerabilities. Industry security analyses from Microsoft, Google (Chromium and Android), and Apple consistently reveal a staggering empirical reality: approximately 70% of all high-severity, remotely exploitable security vulnerabilities stem directly from memory corruption flaws—specifically Spatial safety violations (buffer out-of-bounds reads/writes) and Temporal safety violations (Use-After-Free, double free).
Software-based mitigations—such as Address Space Layout Randomization (ASLR), stack canaries, control-flow integrity (CFI), and software sanitizers like AddressSanitizer (ASan)—have raised the barrier to exploitation.
However, software sanitizers incur severe runtime CPU overheads (often 2x to 3x slowdowns) and heavy memory bloat (2x to 4x RAM), rendering them strictly confined to developer testing rather than production deployment.
The Armv9 Memory Tagging Extension (MTE), originally specified in the Armv8.5-A architecture and mandated as a premier hardware security pillar across modern Armv9 silicon (including Google Tensor G3/G4/G5, MediaTek Dimensity 9300/9400, and Qualcomm Snapdragon platforms), represents a monumental architectural breakthrough.
By implementing hardware-assisted lock-and-key memory tagging directly within CPU execution pipelines and DRAM memory controllers, Armv9 detects spatial and temporal memory violations at runtime with negligible CPU overhead (<2.5%) and bounded memory overhead (~3%).
Production mobile operating systems, led by Android 14, 15, and 16, now deploy hardware MTE directly in production user-space processes and the Linux kernel, transforming elusive zero-day memory corruption exploits into deterministic, immediate hardware crash traps.
+---------------------------------------------------------------------------------------------------+
|                        ARMv9 HARDWARE MEMORY TAGGING PIPELINE (MTE)                               |
+---------------------------------------------------------------------------------------------------+
|  [64-Bit Virtual Memory Address Pointer (TBI Enabled)]                                            |
|  +--------------------+-----------------------------------------------------------------------+  |
|  | Bits [63:60]: RSVD | Bits [59:56]: Logical Tag (4 Bits: 0x0 to 0xF) | Bits [55:0]: VA Bits |  |
|  +--------------------+------------------------------------------------+----------------------+  |
|                                                |                                                  |
|                                                v                                                  |
|  [CPU LOAD / STORE EXECUTION PIPELINE]                                                            |
|  +---------------------------------------------------------------------------------------------+  |
|  | Armv9 Core Tag Checker: Compares Logical Tag against Physical Allocation Tag                |  |
|  |                                                                                             |  |
|  |       [Logical Pointer Tag: 0x4]   <==== (Hardware Comparator) ====>   [Allocation Tag: 0x4]|  |
|  |                                                                                             |  |
|  | - MATCH (0x4 == 0x4) : Memory access permitted; Zero CPU cycle penalty                      |  |
|  | - MISMATCH (0x4 != 0x7): Fault Triggered (SIGSEGV / Tag Check Fault Trap)                    |  |
|  +---------------------------------------------------------------------------------------------+  |
|                                                                                |                  |
|                                                                                v                  |
|  [PHYSICAL MEMORY HIERARCHY: 16-BYTE GRANULES]                                                    |
|  +---------------------------------------------------------------------------------------------+  |
|  | Granule 0 (16 Bytes)  | Tag 0x4 (Stored in Dedicated Tag RAM / Hidden DRAM ECC Bits)         |  |
|  | Granule 1 (16 Bytes)  | Tag 0x4                                                              |  |
|  | Granule 2 (16 Bytes)  | Tag 0x7 (Adjacent Heap Chunk / Previously Freed Memory)             |  |
|  +---------------------------------------------------------------------------------------------+  |
+---------------------------------------------------------------------------------------------------+
1. Hardware Architectural Mechanics: Pointer Tags and Memory Granules
The fundamental premise of Armv9 MTE is modeled on the classical computer science concept of lock-and-key tagged memory:
The Dual-Tag Architecture
MTE partitions the memory safety problem into two distinct, hardware-tracked entities:
- The Logical Tag (The Key): A 4-bit value stored directly within the unused upper bits of a 64-bit virtual memory address pointer. This leverages the 64-bit Arm architecture's native Top-Byte-Ignore (TBI) feature, where the CPU's Memory Management Unit (MMU) ignores the highest 8 bits during virtual-to-physical address translation. Bits
[59:56]are reserved exclusively for the 4-bit MTE logical tag, allowing $2^4 = 16$ unique color tags (0x0through0xF). - The Allocation Tag (The Lock): A 4-bit physical metadata tag assigned to every contiguous 16-byte aligned block of memory, formally designated as a Memory Granule.
Physical Tag Storage Implementations
Because every 16 bytes of data requires 4 bits of metadata, MTE introduces an architectural memory overhead of: $$\frac{4\text{ bits}}{16\text{ bytes} \times 8\text{ bits}} = \frac{4}{128} = 3.125%$$
SoC silicon architects implement this physical tag storage through two primary approaches:
- Dedicated Tag Carveout in System RAM: A contiguous 3.125% partition of physical DRAM is reserved at boot time by the firmware/bootloader. The memory controller automatically interleaves tag reads/writes alongside standard 64-byte cache line accesses.
- DRAM Out-of-Band / ECC Bits: In enterprise server silicon (such as Neoverse cores), spare ECC check bits embedded directly within DDR5/LPDDR5 memory channels are repurposed to store allocation tags, eliminating separate memory controller transactions.
+-----------------------------------------------------------------------+
|                    ARMv9 MTE MEMORY INSTRUCTION EXTENSIONS            |
+-----------------------------------------------------------------------+
| Opcode    | Assembly Syntax    | Operational Description              |
+-----------+--------------------+--------------------------------------+
| IRG       | irg Xd, Xn         | Insert Random Tag: Generates 4-bit   |
|           |                    | random tag into pointer Xd from Xn   |
| STG       | stg Xt, [Xn]       | Store Tag: Writes allocation tag     |
|           |                    | from Xt into memory granule at Xn    |
| ST2G      | st2g Xt, [Xn]      | Store Tag Pair: Writes tag into two  |
|           |                    | consecutive 16-byte granules (32B)   |
| STZG      | stzg Xt, [Xn]      | Store Tag and Zero: Zeroes 16B memory|
|           |                    | and sets matching allocation tag     |
| LDG       | ldg Xt, [Xn]       | Load Tag: Reads 4-bit allocation tag |
|           |                    | from memory into target register Xt  |
+-----------------------------------------------------------------------+
Hardware Comparator Verification
Whenever the CPU executes a memory dereference instruction (LDR, STR, LDP, STP), the core's load/store execution unit extracts bits [59:56] from the effective address register and simultaneously reads the allocation tag assigned to the targeted 16-byte physical granule.
If the 4-bit Logical Tag matches the 4-bit Allocation Tag, the memory transaction proceeds down the L1 data cache pipeline with zero execution stall cycles. If the tags do not match, the core flags a Tag Check Fault (TCF).
2. Operating Modes: Synchronous, Asynchronous, and Asymmetric Execution
A critical engineering innovation of Armv9 MTE is its configurable hardware fault-reporting pipeline. Systems architects can trade off immediate vulnerability diagnostics against extreme CPU execution efficiency across three operating modes:
+-----------------------------------------------------------------------------------------+
|                    ARMv9 MTE OPERATING MODES COMPARISON MATRIX                          |
+-----------------------------------------------------------------------------------------+
| Feature / Mode      | Synchronous (Sync)    | Asynchronous (Async)  | Asymmetric (Asymm) |
+---------------------+-----------------------+-----------------------+--------------------+
| Fault Detection     | Exact instruction     | Deferred / Aggregated | Reads: Exact       |
|                     | boundary              | (Kernel interrupt)    | Writes: Deferred   |
| CPU Overhead        | 2.0% - 5.0%           | 0.5% - 1.5%           | 1.0% - 2.5%        |
| Core Trap Type      | Synchronous Data Abort| Asynchronous Fault Reg| Mixed Trap Pipeline|
| Debug Precision     | Exact PC & Fault Addr | Thread context only   | High on read paths |
| Production Fit      | Security Enclaves /   | Fleet-Wide Telemetry /| Production Mobile  |
|                     | High-Value Daemons    | Battery-Critical Apps | Default (Android)  |
+-----------------------------------------------------------------------------------------+
1. Synchronous Mode (MTE Sync)
In Synchronous Mode, the CPU halts execution immediately on the exact instruction that attempted the invalid memory access.
- The kernel receives a synchronous data abort, identifies the faulting instruction pointer (PC), and delivers a
SIGSEGVsignal to the process with codeSEGV_MTESERR(Memory Tagging Error Synchronous). - The crash tombstone records the exact line of code, the invalid pointer tag, and the existing memory allocation tag.
- While providing impeccable debugging fidelity, Synchronous Mode enforces pipeline serialization, introducing a modest 2% to 5% CPU execution overhead.
2. Asynchronous Mode (MTE Async)
In Asynchronous Mode, tag checking is performed out-of-band by the memory subsystem without stalling the CPU core pipeline:
- When a tag mismatch occurs, the hardware does not interrupt execution immediately. Instead, it sets a sticky bit in a processor system register (
TFSRE0_EL1/TFSR_EL1). - The kernel inspects this register periodically or during scheduled context switches.
- If a fault bit is asserted, the kernel terminates the process asynchronously.
- Asynchronous Mode incurs near-zero runtime overhead (<1% CPU), making it ideal for continuous, fleet-wide vulnerability telemetry across millions of production consumer devices.
3. Asymmetric Mode (MTE Asymm)
Introduced in Armv8.7-A and standard in Armv9, Asymmetric Mode provides the optimal production compromise:
- Memory Reads execute in Synchronous Mode: Because information disclosure and control-flow hijacking frequently start by reading corrupted pointers or uninitialized buffers, read violations trap immediately with full register state.
- Memory Writes execute in Asynchronous Mode: Write operations run without pipeline stalling, buffering any tag check fault in hardware registers.
- Android 15 and 16 select Asymmetric Mode as the default configuration for system daemons, achieving sub-2% real-world CPU impact.
3. Threat Vectors Mitigated: Spatial vs. Temporal Memory Exploitation
To appreciate how MTE transforms exploit engineering, consider the mechanics of the two most prevalent memory corruption vulnerability classes:
Spatial Safety Violations (Heap & Stack Buffer Overflows)
A buffer overflow occurs when a thread writes or reads beyond the allocated bounds of an object:
// Vulnerable C Snippet: Linear Buffer Overflow
char *buffer = (char *)malloc(32); // Allocates two 16-byte granules (Granule 0, 1)
// Scudo allocator tags Granule 0 and Granule 1 with Tag 0x3.
// Adjacent memory (Granule 2) belongs to another object, tagged with Tag 0x8.

// Pointer returned to application: 0x0300007b8a124000 (Tagged with 0x3)
buffer[35] = 'A'; // Writes to byte offset 35 (inside Granule 2)
+-----------------------------------------------------------------------------------------+
|                        SPATIAL BUFFER OVERFLOW DETECTION                                |
+-----------------------------------------------------------------------------------------+
|  Memory Granule 0 [0..15]   : Tag 0x3  <=== Buffer Pointer (Tag 0x3) -> VALID           |
|  Memory Granule 1 [16..31]  : Tag 0x3  <=== Buffer Pointer (Tag 0x3) -> VALID           |
|  Memory Granule 2 [32..47]  : Tag 0x8  <=== Buffer Pointer (Tag 0x3) -> MISMATCH!      |
|                                             [Hardware Trap: 0x3 != 0x8 => SIGSEGV]      |
+-----------------------------------------------------------------------------------------+
When buffer[35] is dereferenced, the CPU compares the pointer's logical tag (0x3) with Granule 2's allocation tag (0x8). The mismatch triggers an immediate hardware trap before memory is corrupted.
Temporal Safety Violations (Use-After-Free)
A Use-After-Free (UAF) occurs when an application continues to dereference a pointer after freeing the underlying object:
+---------------------------------------------------------------------------------------------------+
|                        TEMPORAL USE-AFTER-FREE (UAF) MITIGATION                                   |
+---------------------------------------------------------------------------------------------------+
|  1. MALLOC:                                                                                       |
|  App allocates Object A (32B). Allocator assigns Tag 0x5 to Granules and Pointer.                 |
|  Pointer A = 0x0500007B...                                                                        |
|                                                                                                   |
|  2. FREE:                                                                                         |
|  App calls free(Pointer A).                                                                       |
|  Scudo allocator re-tags the memory granules with a NEW RANDOM TAG: Tag 0xB.                      |
|                                                                                                   |
|  3. DANGLING DEREFERENCE:                                                                         |
|  Attacker attempts to write via stale Pointer A (which still carries Tag 0x5):                    |
|                                                                                                   |
|       Pointer Tag: 0x5  <======== (MISMATCH!) ========>  Memory Allocation Tag: 0xB               |
|                                                                                                   |
|  [Result: Hardware Comparator halts execution instantly. UAF primitive neutralized.]             |
+---------------------------------------------------------------------------------------------------+
Because the allocator retags the memory granules immediately upon deallocation, any subsequent read or write using the stale pointer fails with a 93.75% probability per access ($15/16$). In practical exploit chains where multiple accesses occur, the probability of bypassing MTE drops exponentially: $$P(\text{Bypass}) = \left(\frac{1}{16}\right)^N$$ For a sequence of just 3 accesses, the bypass probability is less than $0.024%$.
4. Allocator Architecture: Scudo Hardened Memory Allocator Internals
Operating-system-level support for MTE requires intimate cooperation between the kernel and the user-space memory allocator. Android and modern Linux distributions deploy Scudo, an LLVM-maintained hardened memory allocator designed explicitly to leverage Armv9 MTE hardware primitives.
+-----------------------------------------------------------------------------------------+
|                    SCUDO ALLOCATOR CHUNK WITH 16-BYTE TAG GRANULES                      |
+-----------------------------------------------------------------------------------------+
| [Chunk Header (16B)] : Tag 0x1 (Checksum, Class ID, Size Offset, State)                 |
+-----------------------------------------------------------------------------------------+
| [User Data 0 (16B)]  : Tag 0x4                                                          |
| [User Data 1 (16B)]  : Tag 0x4                                                          |
| [User Data 2 (16B)]  : Tag 0x4 (Allocated object payload, all granules tagged 0x4)      |
+-----------------------------------------------------------------------------------------+
| [Tail Padding (16B)] : Tag 0x9 (Colored with distinct tag to catch off-by-one writes)   |
+-----------------------------------------------------------------------------------------+
Scudo Tagging Algorithms
When an application invokes malloc(size):
- Granule Alignment: Scudo rounds the requested size up to the nearest 16-byte multiple.
- Tag Generation (
IRG): Scudo issues the Armv9IRG(Insert Random Tag) assembly instruction, which queries the hardware Pseudo-Random Number Generator (PRNG) to generate a random 4-bit tag distinct from the previous tag used at that address. - Bulk Memory Tagging (
STZG): Scudo utilizes theSTZG(Store Allocation Tag and Zero) instruction to write the 4-bit allocation tag across all memory granules while simultaneously zero-initializing memory, executing tag storage and cache initialization in a single hardware cycle. - Header Protection: The chunk header preceding the allocation is colored with a completely separate tag, ensuring that heap-header overwrites trap instantly.
5. Linux Kernel & Android Systems Hardening Playbook
Deploying Armv9 MTE across production services requires precise kernel configuration and programmatic control.
Step 1: Kernel Boot Parameters and Hardware Verification
Verify that the host CPU supports MTE and ensure kernel support is enabled:
# Verify Armv9 MTE hardware capability flag in cpuinfo
grep -E "mte" /proc/cpuinfo

# Inspect kernel dmesg for MTE initialization
dmesg | grep -i "Memory Tagging Extension"
To configure system-wide MTE behavior on Linux kernels (6.1 through 6.12+), specify the boot argument:
# Set default kernel MTE mode (sync, async, or asymm)
mte=asymm
Step 2: Programmatic User-Space MTE Activation via prctl
Applications configure their desired MTE execution profile at runtime using the Linux prctl() interface:
#include <sys/prctl.h>
#include <stdio.h>
#include <stdlib.h>

#define PR_SET_TAGGED_ADDR_CTRL 55
#define PR_TAGGED_ADDR_ENABLE   (1UL << 0)
#define PR_MTE_TCF_SHIFT        1
#define PR_MTE_TCF_SYNC         (1UL << PR_MTE_TCF_SHIFT)
#define PR_MTE_TCF_ASYNC        (2UL << PR_MTE_TCF_SHIFT)
#define PR_MTE_TCF_ASYMM        (3UL << PR_MTE_TCF_SHIFT)
#define PR_MTE_TAG_MASK         (0xffffUL << 3) // Enable all 16 tags

void enable_mte_synchronous(void) {
    if (prctl(PR_SET_TAGGED_ADDR_CTRL,
              PR_TAGGED_ADDR_ENABLE | PR_MTE_TCF_SYNC | (0xfffeUL << 3),
              0, 0, 0) < 0) {
        perror("MTE initialization failed: Hardware not supported");
        exit(1);
    }
    printf("Armv9 MTE Synchronous enforcement active.\n");
}
Step 3: Android App Manifest Hardening
Android enables per-application MTE configuration without code recompilation. In AndroidManifest.xml:
<application
    android:name=".ProductionService"
    android:memtagMode="asymmetric">
</application>
Values for android:memtagMode include:
off: Disables MTE entirely.asymmetric: Recommended production default (Sync reads, Async writes).sync: Maximum security for financial and authentication modules.
6. Architectural FAQ: Common Questions on Armv9 MTE
Q1: Can an attacker bypass MTE by guessing the 4-bit tag?
The 4-bit tag provides $2^4 = 16$ possible colors. A single blind memory access has a $1/16$ ($6.25%$) probability of matching the allocation tag. However, modern exploit primitives require multi-step pointer chasing, heap spray alignment, and consecutive memory dereferences. For an exploit requiring 4 consecutive accesses, the probability of escaping detection is $(1/16)^4 \approx 0.0015%$. Any single mismatch crashes the process immediately, alerting security monitoring.
Q2: Does MTE protect against stack buffer overflows?
Yes. While early implementations focused on heap allocations via Scudo, the LLVM compiler toolchain includes stack-tagging instrumentation. Compilers allocate stack frames in 16-byte granules and assign distinct random tags to local stack buffers.
Q3: What is the exact difference between ASan, HWASan, and MTE?
ASan (AddressSanitizer) uses compiler-generated shadow memory and redzones, incurring a ~2x CPU slowdown and 2x–3x RAM bloat. HWASan (Hardware-assisted ASan) uses pointer tagging via Top-Byte-Ignore (TBI) but emulates tag checks in software, reducing overhead to ~40% CPU. Armv9 MTE implements tag comparisons directly in CPU hardware silicon and memory controllers, reducing overhead to <2.5% CPU, enabling real-world production deployment.
Q4: Does MTE introduce memory fragmentation?
Because MTE enforces a minimum 16-byte alignment granule, allocations smaller than 16 bytes (or allocations not divisible by 16) suffer from small internal fragmentation. In real-world workloads, Scudo's memory overhead with MTE enabled averages between 3% and 5% total heap bloat.
Q5: Can MTE be used alongside Kernel Address Space Layout Randomization (KASLR)?
Yes. MTE and KASLR operate at completely independent architectural layers. KASLR randomizes base kernel virtual addresses to hinder ROP gadget location, while MTE enforces fine-grained granule-level access permissions, providing defense-in-depth.