

Web performance
Cross-Origin Storage API Ends Duplicate AI and Wasm Downloads: Architecture, Privacy Gates, and Implementation
Chrome for Developers' Cross-Origin Storage (COS) API lets websites share SHA-256 cached AI models, Wasm runtimes, and web fonts across origins without breaking cache partitioning privacy. Learn how the Public Hash List gate works and implement a progressive-enhancement SRI loader.
8 min read
Cross-Origin Storage API Ends Duplicate AI and Wasm Downloads: Architecture, Privacy Gates, and Implementation
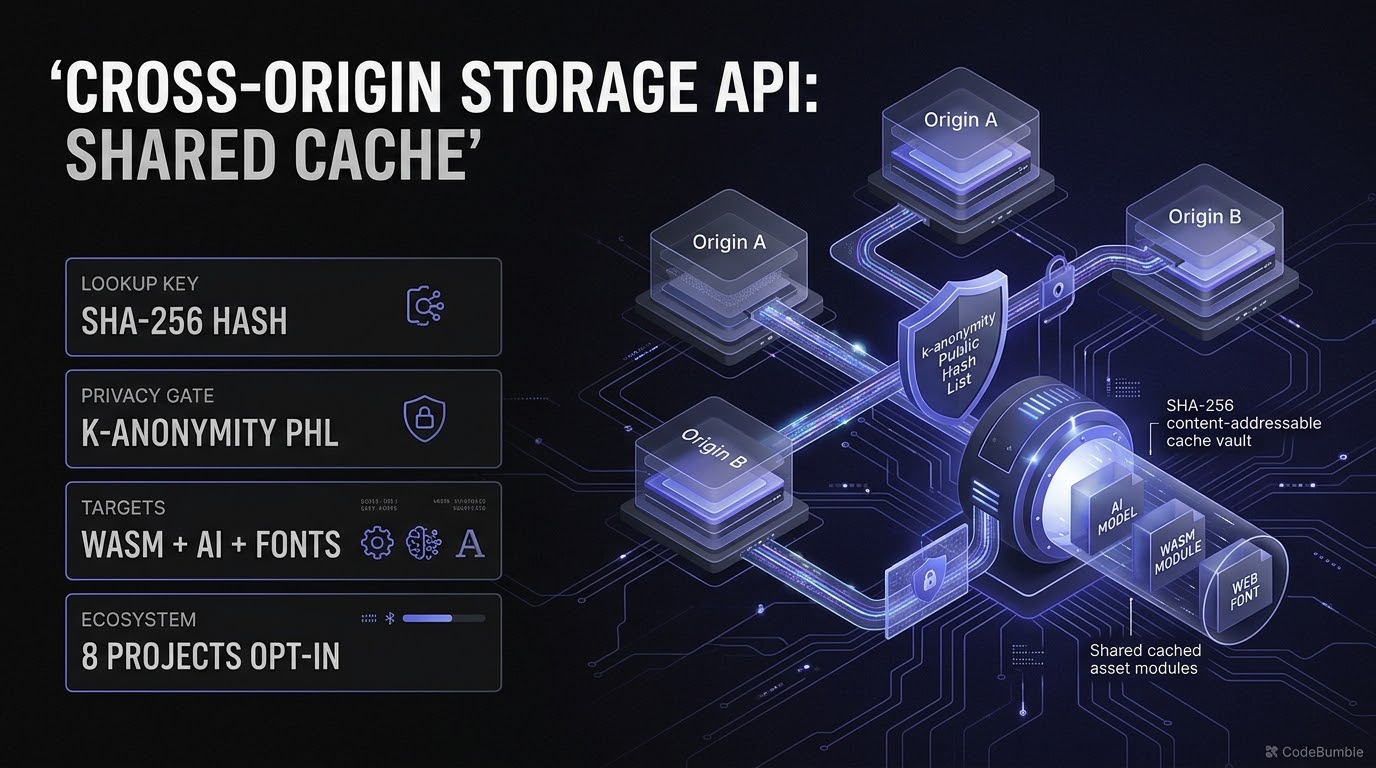
Executive Summary
Since browsers introduced HTTP cache partitioning by top-level origin to block cross-site tracking and timing side-channel attacks, web performance engineers have paid a steep bandwidth and latency tax: if Site A and Site B load the exact same byte-identical WebAssembly runtime, web font, or client-side AI model, the browser must download and store it twice. On November 10, 2026 (surfaced across search and web-platform engineering digests on November 13), Chrome for Developers published Introducing the Cross-Origin Storage API, detailing an early-stage WICG specification for a content-addressable shared browser cache.
Instead of keying cached assets by URL and top-level origin, the Cross-Origin Storage (COS) API (navigator.crossOriginStorage) identifies resources by their SHA-256 cryptographic hash. Once stored by one origin, any authorized origin—or any origin globally if the asset clears a k-anonymity-style Public Hash List (PHL)—can retrieve the file handle locally without a second network transfer.
For web performance teams shipping gigabyte-scale WebGPU/WebML models, Flutter Skia Wasm bundles, or multi-megabyte game engines, COS promises to eliminate redundant cold-start downloads. However, because no browser ships native COS support yet (testing currently relies on browser polyfill extensions and prototype builds in Servo and Ladybird), teams must implement COS strictly as a progressive enhancement layered over standard Cache Storage / Origin Private File System (OPFS) fallbacks.
The 5 High-Impact Asset Types Targeted by Cross-Origin Storage
Per Chrome for Developers and the WICG Cross-Origin Storage specification, COS targets five specific asset classes where HTTP cache partitioning creates severe duplicate-download overhead:
| Asset Category | Typical Payload Size | Example Ecosystem Adopters (Experimental) | Primary Performance Impact |
|---|---|---|---|
| 1. Client-Side AI Models | ~1 GB to tens of GB (Gemma, Llama) |
Transformers.js, WebLLM, wllama, Prompt API Polyfill |
Eliminates multi-GB cold-start re-downloads across Web ML apps |
| 2. WebAssembly (Wasm) Modules | Several MB to tens of MB |
Flutter (Skia Wasm runtime), Emscripten |
Shares byte-identical runtimes requested millions of times daily |
| 3. JavaScript Libraries & Frameworks | Hundreds of KB (untreeshaken vendor) |
Nuxt.js (Vite COS plugin), Prebid.js COS CDN |
Reuses complete vendor bundles (e.g., React) across distinct origins |
| 4. Browser Game Engines | Tens of MB |
Godot, Unity web runtimes |
Gaming portals share one engine runtime; fetch only game assets |
| 5. Large Web Fonts | 1 MB–10+ MB |
Icon fonts, emoji fonts, broad Unicode fonts | Cuts First Contentful Paint (FCP) / LCP font-swap stalls across sites |
Technical Mechanics and Architecture
How Content-Addressable Lookup and k-Anonymity Privacy Gates Work
The central security challenge of any cross-origin cache is history sniffing: if Site B can probe whether a specific file hash exists in the user's cache, Site B might infer that the user previously visited Site A. As documented in the WICG Cross-Origin Storage spec and W3C TAG Design Review, COS prevents tracking through three layered boundaries:
+-----------------------------------------------------------------------------+
|        CROSS-ORIGIN STORAGE (COS): CONTENT-ADDRESSABLE CACHE & PRIVACY      |
+-----------------------------------------------------------------------------+
|                                                                             |
|  [ ORIGIN A (Stores Resource) ]                                             |
|   Fetches asset -> Computes SHA-256 (64-char hex)                           |
|     |-- Default: Same-site readable only                                    |
|     |-- Specific origins: Requires Cross-Origin-Storage-Allow-Origin header |
|     +-- Global (origins: '*'): Subject to Public Hash List (PHL) gate       |
|                                                                             |
|  [ BROWSER COS VAULT (Content-Addressable by SHA-256) ]                     |
|   Privacy Gate:                                                             |
|     |-- Checks Public Hash List (k-anonymity popularity threshold)          |
|     +-- May apply GREASE'ing (random NotFoundError on smaller files)        |
|                                                                             |
|  [ ORIGIN B (Requests Resource) ]                                           |
|   navigator.crossOriginStorage.getFileHandle({ algorithm: "SHA-256", ... }) |
|     |-- HIT  -> Returns local FileSystemFileHandle (0 network bytes!)       |
|     +-- MISS -> Falls back to fetch() + integrity (SRI) + local Cache API   |
+-----------------------------------------------------------------------------+
- Same-Site Default: Omitting
originsrestricts a stored file to same-site origins only—ideal for sharing assets across an organization's own subdomains. - Explicit Origin Lists: Passing
origins: ['https://app.example']requires the asset server to authorize each listed origin via theCross-Origin-Storage-Allow-OriginHTTP response header. - Global Sharing (
origins: '*') & Public Hash List (PHL): Only hashes that clear a k-anonymity popularity threshold on the Public Hash List can be disclosed globally across arbitrary origins. Browsers may also randomly returnNotFoundError("GREASE'ing") for smaller qualifying files to further obscure cache state.
Defensive & Progressive-Enhancement Code Pattern
Because navigator.crossOriginStorage is an early-stage WICG proposal with no native browser shipment yet, never call it unconditionally. Always feature-detect the API, enforce a strict SHA-256 integrity hash on the network fallback, and catch NotAllowedError and NotFoundError gracefully:
/**
 * Progressive-enhancement loader using Cross-Origin Storage (COS)
 * with Subresource Integrity (SRI) network fallback.
 */
export async function loadSharedAssetWithCOS(assetUrl, sha256Hex, sriBase64) {
  const hashSpec = { algorithm: "SHA-256", value: sha256Hex };

  // 1. Attempt content-addressable lookup if COS (or polyfill) is present
  if ("crossOriginStorage" in navigator) {
    try {
      // Spec surface: getFileHandle() / requestFileHandles()
      const handle = navigator.crossOriginStorage.getFileHandle
        ? await navigator.crossOriginStorage.getFileHandle(hashSpec)
        : (await navigator.crossOriginStorage.requestFileHandles([hashSpec]))[0];

      if (handle) {
        const file = await handle.getFile();
        return await file.arrayBuffer();
      }
    } catch (err) {
      // Expected on cache miss, user denial, or GREASE'ing
      if (err.name !== "NotFoundError" && err.name !== "NotAllowedError") {
        console.warn("[COS] Unexpected lookup error, falling back to network:", err);
      }
    }
  }

  // 2. Fallback: fetch with mandatory Subresource Integrity verification
  const response = await fetch(assetUrl, {
    integrity: `sha256-${sriBase64}`,
    mode: "cors",
  });
  if (!response.ok) {
    throw new Error(`Asset fetch failed: HTTP ${response.status}`);
  }
  return await response.arrayBuffer();
}
Planned Declarative Integrations Across HTML, CSS, and Fetch
Alongside the imperative JavaScript interface, the Chrome team has filed declarative host integrations across four web standards (Chrome for Developers):
- WHATWG HTML:
crossoriginstorageattribute on<link>and<script>, pluscrossOriginStorageimport attribute for ES modules. - CSS Working Group:
cross-origin-storage()request-URL modifier insideurl()(for@font-facerules). - WHATWG Fetch:
crossOriginStorageoption onRequestInitalongsideintegrity.
Evidence: Standardization Status, Ecosystem Adoption, and Caveats
- Standardization Trajectory: As of November 10–13, 2026, COS is an active WICG proposal (
WICG/cross-origin-storage, spec draft updated November 3, 2026) undergoing early W3C TAG Design Review (w3ctag/design-reviews#1254), with formal standards-position requests filed with Mozilla (#1427) and WebKit (#703), plus cross-browser Web Platform Tests in progress. - Ecosystem Opt-In: Eight open-source projects already ship experimental COS support behind opt-in flags or polyfill extensions: Emscripten, Flutter (Skia Wasm), Transformers.js, WebLLM, wllama, Nuxt.js (maintaining a Vite COS plugin), Prompt API Polyfill, and Prebid.js.
- Confidence Level: High on API design, privacy model (PHL + GREASE'ing), and standardization status (corroborated across Chrome for Developers, WICG spec, and W3C TAG).
- Benchmark Caveat: Neither Chrome for Developers nor the WICG explainer publishes standardized, cross-browser Core Web Vitals (LCP/INP) field benchmarks from production traffic yet, because native browser implementations are still in the Intent to Prototype / polyfill phase.
Web Performance Adoption Playbook
Step 1: Audit Duplicate Third-Party & Vendor Payloads Across Your Origins
Use Chrome DevTools Coverage and Network waterfall exports across your organization's subdomains (app.example.com, docs.example.com, checkout.example.com) to identify large byte-identical assets—especially Wasm runtimes, WebGL/game engines, icon fonts, and client-side ML weights—that are currently re-downloaded per origin due to cache partitioning.
Step 2: Enforce Deterministic Builds & Subresource Integrity (SRI)
COS only deduplicates byte-identical files. Pin exact dependency versions, strip non-deterministic build timestamps from Wasm/JS bundles, and publish SHA-256 hashes for every shared asset so both current SRI fetch() calls and future COS lookups share one canonical digest.
Step 3: Isolate COS Behind Feature Detection & Same-Site Scoping First
When prototyping with the official Cross-Origin Storage browser extension (available for Chrome, Firefox, and Safari), wrap every call in "crossOriginStorage" in navigator feature detection and start with same-site or explicit origins lists (paired with Cross-Origin-Storage-Allow-Origin headers) rather than assuming global Public Hash List eligibility.
Step 4: Pair with Standard HTTP/3, Immutable Cache-Control, and OPFS
Until browsers ship native COS support, continue serving large static assets with Cache-Control: public, max-age=31536000, immutable over HTTP/3 and persist user-downloaded ML weights locally in OPFS or the Cache Storage API for repeat visits to the same origin.
Step 5: Rollback Notes
Because COS is purely additive and non-blocking when wrapped in a try/catch progressive enhancement (falling back to standard fetch(..., { integrity })), disabling an experimental COS plugin (such as the Vite COS plugin in Nuxt.js) requires only toggling the build flag off—zero data migrations or cache invalidations are needed on the client.
Frequently Asked Questions
1. How does the Cross-Origin Storage API avoid breaking browser privacy?
Unlike legacy unpartitioned HTTP caches, COS is content-addressable by SHA-256 hash and enforces a k-anonymity Public Hash List (PHL) gate for globally shared files, plus optional "GREASE'ing" (NotFoundError responses on smaller files) so sites cannot use cache hits to fingerprint a user's browsing history.
2. Is navigator.crossOriginStorage shipped in Chrome Stable today?
No. As of November 2026, Cross-Origin Storage is an early-stage WICG proposal with an Intent to Prototype and a browser extension polyfill for Chrome, Firefox, and Safari (plus personal prototype implementations in Servo and Ladybird).
3. Why does COS matter so much for Web AI and WebAssembly?
Client-side AI models (like Gemma or Llama via Transformers.js and WebLLM) can weigh 1 GB to tens of GB, and Flutter's Skia Wasm runtime is requested millions of times daily across distinct origins. Without COS, cache partitioning forces users to re-download identical multi-megabyte or gigabyte files for every new domain.
4. Can an organization share proprietary assets only across its own domains?
Yes. Omitting origins restricts access to same-site origins by default, and passing an explicit origins array restricts sharing to those listed origins—provided the asset server returns the matching Cross-Origin-Storage-Allow-Origin header.
5. What happens if a file is not in Cross-Origin Storage?
The browser returns NotFoundError (or NotAllowedError if permission is denied), and the application falls back seamlessly to a standard fetch() request with Subresource Integrity (integrity) verification.
Sources
- Chrome for Developers: Introducing the Cross-Origin Storage API — Published November 10, 2026 (featured in Search Engine Roundtable, Nov 13, 2026).
- WICG Specification Draft: Cross-Origin Storage — Updated November 3, 2026.
- GitHub
WICG/cross-origin-storage: Explainer and Extension Polyfill — Accessed November 14, 2026. - W3C TAG Design Review: Cross-Origin Storage (
w3ctag/design-reviews#1254) — Opened August 5, 2026.
Additional Standards Context: HTTP/2 Cache Digests & Server Headers
Drawing inspiration from Cache Digests for HTTP/2 and the WHATWG File System Living Standard, the Cross-Origin Storage API decouples where an asset is hosted from how the browser verifies and reuses it. When sharing proprietary assets across an explicit origins allowlist rather than globally (origins: '*'), asset servers must emit the Cross-Origin-Storage-Allow-Origin response header authorizing each permitted origin, ensuring that private CDN assets cannot be silently read by unauthorized third-party pages.