

Automation
Elecbrakes ICSA-26-323-02: Unauthenticated BLE Flaws (CVSS 9.6) Expose Trailer Brake Controllers
On November 19, 2026, CISA issued advisory ICSA-26-323-02 warning of three critical vulnerabilities (CVSS v3 base score 9.6) in Elecbrakes EB2, VM1, and ELBC2000 trailer brake controllers. Unauthenticated Bluetooth Low Energy command injection and an unprotected firmware-update channel allow in-range attackers to alter braking or disable safety features. While EB2 3.0.4.4.3 and VM1 1.3.4.2.1 ship fixes, the discontinued ELBC2000 currently has no patch.
5 min read
Elecbrakes ICSA-26-323-02: Unauthenticated BLE Flaws (CVSS 9.6) Expose Trailer Brake Controllers
Executive Summary
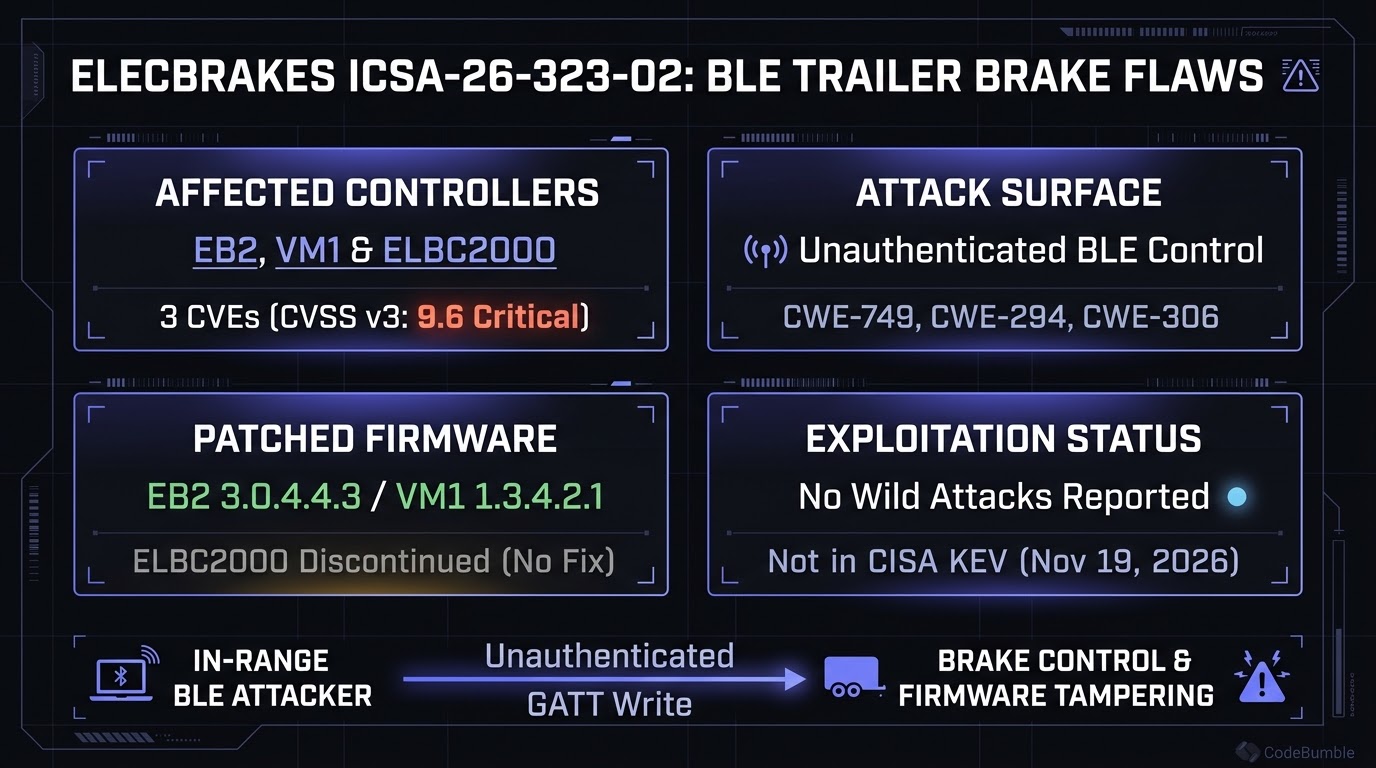
On November 19, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) published Industrial Control Systems Advisory ICSA-26-323-02, detailing three vulnerabilities—CVE-2026-124281, CVE-2026-125273, and CVE-2026-96805—affecting Elecbrakes trailer brake controllers (EB2, VM1, and ELBC2000) (CISA). Rated CVSS v3 base score 9.6 (Critical) on the EB2 controller (Assurant Cyber), the flaws allow an in-range Bluetooth Low Energy (BLE) attacker without authentication or pairing to manipulate braking behavior, modify firmware, or disable brake lights and safety features.
Two operational details make this advisory critical for fleet, commercial towing, and embedded automotive-automation engineers:
- Physical safety impact over adjacent-network BLE: CISA's CVSS v4.0 vector (
CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:L/VI:H/VA:H/SC:L/SI:H/SA:H/S:P) explicitly marks Safety (S:P) and Subsequent System Integrity/Availability (SI:H/SA:H), reflecting the direct physical risk of unauthorized brake actuation on a moving trailer (CISA). - Legacy ELBC2000 remains unpatched: While Elecbrakes has shipped fixed firmware for EB2 (
3.0.4.4.3) and VM1 (1.3.4.2.1) (AI Legal Lab), the predecessor ELBC2000 is no longer sold, and the vendor is still determining how to address the flaws on that hardware (CISA).
Confidence assessment: High confidence on affected models, version bounds (EB2 <= 3.0.4.2.0, VM1 < 1.3.4.2.1, ELBC2000 all versions), CWE classes (CWE-749, CWE-294, CWE-306), and CVSS v4.0 vector (sourced directly from CISA ICSA-26-323-02, NIST NVD, and OffSeq Threat Radar). Note that OffSeq's automated summary initially noted no CVSS score in its preview, whereas CISA's advisory and Assurant Cyber report CVSS v3 9.6 alongside CISA's CVSS v4.0 vector.
Technical Mechanics and Architecture
Elecbrakes controllers mount on trailers and communicate with a smartphone app or cabin remote over Bluetooth Low Energy (BLE) to adjust proportional braking gain, manual override, and diagnostic telemetry. According to CISA ICSA-26-323-02 and OffSeq Threat Radar, the three CVEs stem from missing authentication, replayable commands, and an unprotected OTA firmware-update channel:
- Missing Authentication for Critical Function (
CWE-306) & Exposed Dangerous Method (CWE-749): An unauthenticated command-injection flaw lets any in-range BLE device write directly to the controller's GATT control interface and influence braking without pairing or cryptographic authentication. - Authentication Bypass by Capture-Replay (
CWE-294): Lack of per-session nonces or cryptographic sequence validation allows captured BLE control frames to be replayed. - Unprotected Firmware-Update Channel: Over-the-air (OTA) firmware updates lack sufficient integrity and origin verification, permitting unauthorized firmware modification on exposed controllers.
+-----------------------+       BLE Adjacent Range       +-------------------------------+
|  In-Range Attacker    | -----------------------------> |  Elecbrakes Controller        |
|  (No Pairing / Auth)  |   1. Unauthenticated GATT      |  (EB2 <= 3.0.4.2.0,           |
+-----------------------+      Control Write             |   VM1 < 1.3.4.2.1, ELBC2000)  |
                            2. Replay / Unprotected OTA  +---------------+---------------+
                                                                         |
                                 +---------------------------------------+---------------------------------------+
                                 |                                       |                                       |
                                 v                                       v                                       v
                       +-------------------+                   +-------------------+                   +-------------------+
                       | Brake Control     |                   | Brake Lights &    |                   | Unauthorized      |
                       | Manipulation      |                   | Safety Disable    |                   | Firmware Flash    |
                       +-------------------+                   +-------------------+                   +-------------------+
Safe Defensive Firmware & BLE Architecture Pattern
For embedded engineers designing BLE-connected OT, fleet, or industrial actuators, never rely on BLE "obscurity" or unauthenticated GATT characteristics. Enforce LE Secure Connections pairing with authenticated GATT writes, plus cryptographically signed OTA images and monotonic anti-replay counters:
#include <stdbool.h>
#include <stdint.h>

/* Safe defensive pattern: verify BLE link security + monotonic sequence + signature */
bool validate_ble_actuator_cmd(bool is_encrypted_mitm_link,
                               uint32_t msg_seq, uint32_t *last_valid_seq,
                               bool hmac_verified) {
    if (!is_encrypted_mitm_link || !hmac_verified || last_valid_seq == NULL) {
        return false;
    }
    /* Prevent CWE-294 capture-replay attacks */
    if (msg_seq <= *last_valid_seq) {
        return false;
    }
    *last_valid_seq = msg_seq;
    return true;
}
Evidence: Affected Versions, Exploitation Status, and Benchmarking Gaps
Affected Products and Fixed Firmware
| Model | Affected Versions | Fixed Version | Source |
|---|---|---|---|
| Elecbrakes EB2 | <= 3.0.4.2.0 |
3.0.4.4.3 |
CISA, AI Legal Lab |
| Elecbrakes VM1 | < 1.3.4.2.1 |
1.3.4.2.1 |
CISA, AI Legal Lab |
| Elecbrakes ELBC2000 | All versions (vers:all/*) |
No fix yet (discontinued) | CISA |
Exploitation Status and Benchmarks
- Exploitation evidence: As of November 19, 2026, OffSeq Threat Radar reports no public exploit code indexed in Metasploit or Exploit-DB, no public Nuclei templates, no CISA KEV listing, and no observed attack traffic in the wild.
- Performance and latency benchmarks: Neither Elecbrakes nor CISA publishes BLE connection latency, OTA update duration, or microcontroller CPU overhead figures for
EB2 3.0.4.4.3orVM1 1.3.4.2.1. Fleet operators should verify update completion and brake calibration on a single stationary trailer before rolling out across a fleet.
Hardening Playbook
Audit fleet and trailer controller inventory Inspect all commercial and utility trailers equipped with Elecbrakes units to identify exact hardware models (EB2, VM1, or ELBC2000) and current firmware versions via the Elecbrakes management interface.
Apply vendor firmware updates immediately (
EB2andVM1)- Update EB2 units from
<= 3.0.4.2.0to3.0.4.4.3or later. - Update VM1 units below
1.3.4.2.1to1.3.4.2.1or later. Follow Elecbrakes' remote-upgrade procedure (elecbrakes.com/remote-upgrade) while trailers are parked and stationary (OffSeq Threat Radar).
- Update EB2 units from
Mitigate or retire unpatched
ELBC2000units Because ELBC2000 is discontinued and has no firmware fix yet, assess physical risk in high-density depots, public highways, or sensitive logistics yards. Where feasible, schedule hardware replacement with patched EB2 or VM1 controllers.Monitor for anomalous BLE activity in fleet depots In commercial yards or staging areas, log unauthorized BLE GATT connection attempts or unexpected brake-controller resets, and ensure maintenance tablets used for OTA updates are enrolled in MDM with up-to-date OS patches.
Post-update brake verification and rollback note After flashing
EB2 3.0.4.4.3orVM1 1.3.4.2.1, perform a stationary manual brake-light and proportional-gain check before returning the trailer to road service. Rollback note: Do not downgrade firmware back toEB2 <= 3.0.4.2.0orVM1 < 1.3.4.2.1, as doing so re-exposes the unauthenticated BLE control and OTA channels.
Frequently Asked Questions (FAQ)
1. Can an attacker exploit Elecbrakes ICSA-26-323-02 over the internet?
No. The vulnerabilities require adjacent network (AV:A) Bluetooth Low Energy (BLE) range—meaning the attacker must be physically near the trailer controller (CISA).
2. Does the attacker need to pair with the Elecbrakes controller first?
No. CISA states the unauthenticated command injection allows an in-range BLE device to write to the control interface and influence braking with no authentication or pairing (CISA).
3. Which Elecbrakes firmware versions fix the vulnerabilities?
EB2 3.0.4.4.3 and VM1 1.3.4.2.1 include the fixes (AI Legal Lab).
4. Is there a patch for the Elecbrakes ELBC2000?
Not at this time. The ELBC2000 is no longer sold, and CISA notes the vendor is still determining how to address these vulnerabilities for that controller (CISA).
5. Are these Elecbrakes flaws being actively exploited in the wild?
No. As of November 19, 2026, no active exploitation, public Metasploit modules, or CISA KEV listings have been reported (OffSeq Threat Radar).
Sources
- CISA — ICS Advisory ICSA-26-323-02: Elecbrakes EB2, VM1, ELBC2000 (November 19, 2026)
- NIST NVD — CVE-2026-96805 Detail (November 21, 2026)
- Assurant Cyber — Elecbrakes EB2, VM1, ELBC2000 (ICSA-26-323-02) (November 20, 2026)
- OffSeq Threat Radar — Elecbrakes EB2, VM1, ELBC2000 (November 19, 2026)
- AI Legal Lab — Vulnerability News: Elecbrakes EB2, VM1 and ELBC2000 (November 19, 2026)