

Device
Zyxel Patches Critical 9.8 Firmware Flaw (CVE-2026-79614) Across 48 CPE, ONT, and Wi-Fi Devices
Zyxel patched CVE-2026-79614 (CVSS 9.8 unauthenticated out-of-bounds write in libclinkc.so) and CVE-2026-86676 (CVSS 7.2 post-auth CGI command injection) across 48 DSL/Ethernet CPE, Fiber ONT, and Wireless Extender models on November 17, 2026. Review affected firmware, ISP update caveats, and WAN hardening steps.
7 min read
Zyxel Patches Critical 9.8 Firmware Flaw (CVE-2026-79614) Across 48 CPE, ONT, and Wi-Fi Devices
Executive Summary
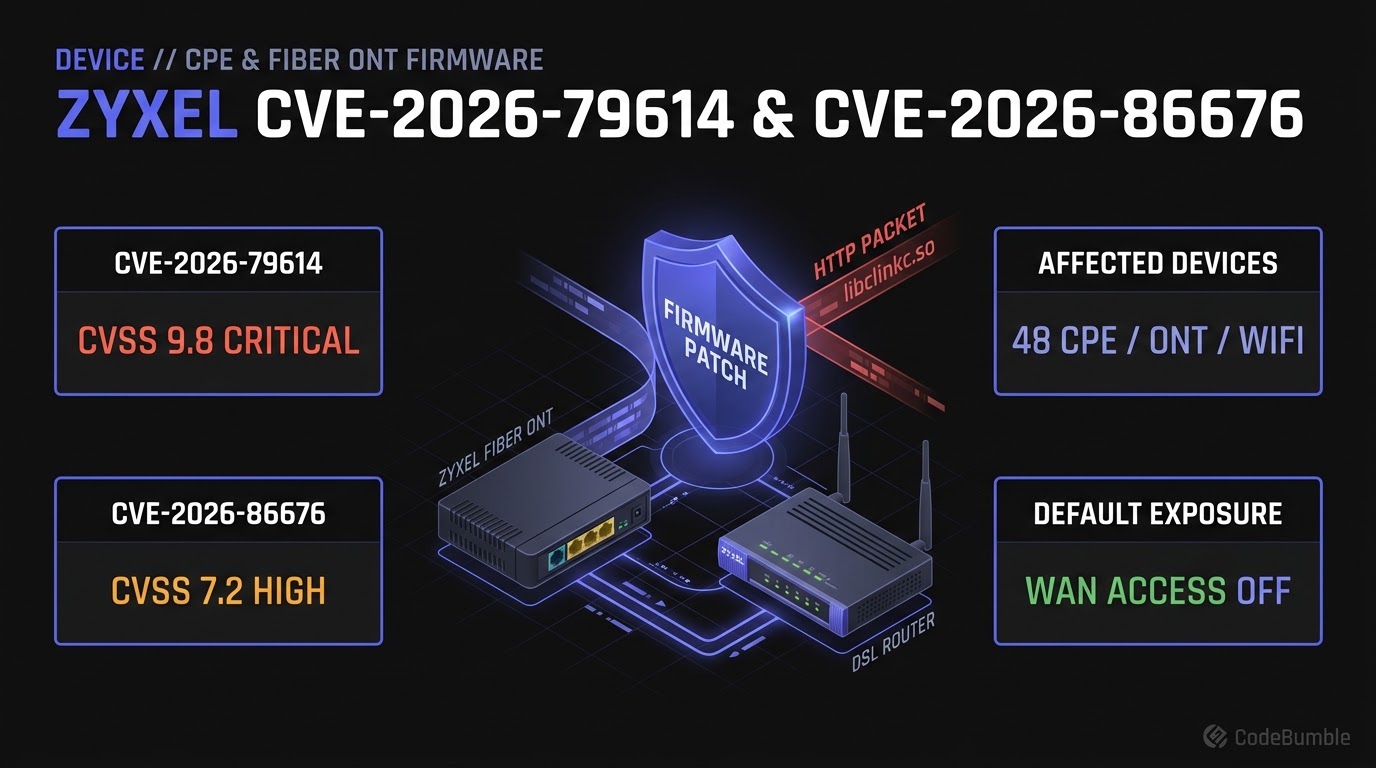
On November 17, 2026, Zyxel Networks published a coordinated security advisory addressing two vulnerabilities across its service-provider and enterprise edge hardware: CVE-2026-79614 (CVSS 3.1 9.8 Critical), an unauthenticated out-of-bounds write in libclinkc.so, and CVE-2026-86676 (CVSS 3.1 7.2 High), a post-authentication OS command injection flaw in a CGI handler. The same day, both the Canadian Centre for Cyber Security (AV26-1167) and Spain's INCIBE-CERT issued corresponding alerts urging administrators and ISPs to deploy the patched firmware releases.
CVE-2026-79614 affects 48 distinct Zyxel hardware models—36 DSL/Ethernet CPE gateways, 8 Fiber ONTs, and 4 Wireless Extenders—while CVE-2026-86676 affects 29 models across those same product lines. Zyxel notes that WAN management access is disabled by default on these devices, meaning remote internet-facing exploitation requires either an administrator or ISP to have enabled WAN HTTP access, or an attacker to reach the management interface from the local LAN/VLAN.
Confidence Level: High. Affected model lists, firmware patch versions, root-cause component names, and default WAN posture are verified directly from Zyxel's November 17, 2026 advisory and corroborated by CCCS (AV26-1167), INCIBE-CERT, and Tenable CVE records. No active exploitation in the wild has been reported in these advisories as of November 18, 2026.
Technical Mechanics & Architecture
Customer-premises equipment (CPE), Fiber ONTs, and wireless extenders typically run embedded Linux distributions with lightweight C-based HTTP/UPnP/TR-069 daemons and CGI web management interfaces. Both vulnerabilities disclosed on November 17, 2026 stem from memory-unsafety and input-sanitization flaws in those embedded web-management layers.
CVE-2026-79614: Unauthenticated Out-of-Bounds Write in libclinkc.so
Reported by security researcher Adam Simuntis, CVE-2026-79614 carries a CVSS 3.1 Base Score of 9.8 Critical (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H per Tenable and ENISA/CERT-Bund). The flaw resides in libclinkc.so, a shared C library commonly used in Zyxel embedded firmware for HTTP/UPnP protocol handling. By sending a crafted unauthenticated HTTP request to a reachable management interface, an attacker can trigger an out-of-bounds memory write, elevate privileges, and potentially execute arbitrary OS commands on the underlying device.
CVE-2026-86676: Post-Authentication CGI Command Injection
Reported by researcher Joni Gadd, CVE-2026-86676 carries a CVSS 3.1 Base Score of 7.2 High. It resides in the Description parameter of a CGI program in Zyxel's web administration interface. An attacker who already holds administrator credentials (for example, via credential reuse, weak default passwords, or a prior session compromise) can inject OS commands via a crafted HTTP request.
+-----------------------------------------------------------------------+
|                NETWORK EXPOSURE PATHS (CPE / ONT / WIFI)              |
|                                                                       |
|  [ Untrusted LAN / Guest Wi-Fi ]        [ WAN Interface (Internet) ]  |
|  (Default reachable surface)            (WAN HTTP OFF by default;     |
|                                          exposed if ISP/admin enabled)|
+---------------+-----------------------------------+-------------------+
                |                                   |
                +-----------------+-----------------+
                                  |
                                  v
+-----------------------------------------------------------------------+
|             ZYXEL EMBEDDED HTTP / CGI MANAGEMENT STACK                |
|                                                                       |
|  1. CVE-2026-79614 (CVSS 9.8, Pre-Auth):                              |
|     Crafted HTTP request -> libclinkc.so -> Out-of-bounds write -> RCE|
|                                                                       |
|  2. CVE-2026-86676 (CVSS 7.2, Post-Auth):                             |
|     Admin HTTP request -> CGI "Description" param -> OS Command Inj.  |
+---------------------------------+-------------------------------------+
                                  |
                                  v
+-----------------------------------------------------------------------+
|             DEFENSIVE BOUNDARY (PATCH + NETWORK ISOLATION)            |
|  * Upgrade to Zyxel patched firmware (e.g., 5.50(ABVY.8.4)C0)         |
|  * Verify WAN management disabled; isolate management to admin VLAN   |
|  * ISP-supplied hardware: request ISP-customized patched build        |
+-----------------------------------------------------------------------+
Safe Exposure Verification (Read-Only Network Check)
Before assuming a CPE or ONT is safe due to default settings, network engineers should verify that WAN-facing management ports (80, 443, 8080, 8443) are closed from external IP ranges and audit local management reachability:
# Read-only check from an external probe to verify WAN HTTP/HTTPS management is closed
# Expected result: connection refused / filtered (timeout), NOT an HTTP login page
nmap -Pn -p 80,443,8080,8443 <WAN_PUBLIC_IP>
On the LAN side, log into the device's web interface or check the firmware banner to compare the installed firmware string (for example, 5.50(ABVY.8.3)C0) against Zyxel's November 17 patch matrix.
Evidence & Affected Hardware Matrix
Zyxel's November 17, 2026 advisory lists 48 affected models for CVE-2026-79614 (and 29 of those models—plus Fiber ONT PM5311-T0—for CVE-2026-86676). Crucially, Zyxel notes two distribution caveats:
- ISP-customized firmware: Models supplied by an Internet Service Provider (such as the
EX5601-T1noted by Security.nl for Odido customers) may run ISP-customized builds and must be patched via the ISP rather than generic retail images. - Sales/support distribution: Zyxel directs administrators to contact their Zyxel sales representative or support team to obtain the patched firmware files.
Representative Patched Firmware Matrix (48 Affected Models Summary)
| Device Category | Model Series (Sample of 48 Affected) | Vulnerable Firmware (Through) | Patched Firmware (Nov 17, 2026) |
|---|---|---|---|
| DSL/Ethernet CPE | DX3300-T0, DX3300-T1, DX3301-T0, EX3300-T0, EX3300-T1, EX3301-T0 |
5.50(ABVY.8.3)C0 |
5.50(ABVY.8.4)C0 |
| DSL/Ethernet CPE | DX4510-B0, DX4510-B1 |
5.17(ABYL.10.4)C0 |
5.17(ABYL.10.5)C0 |
| DSL/Ethernet CPE | DX5401-B1, EX5401-B1 |
5.17(ABYO.7.4)C0 |
5.17(ABYO.7.5)C0 |
| DSL/Ethernet CPE | EE3301-00 / EE5301-00 / EE6510-10 |
5.63(ACMU.3.3)C0 / 5.63(ACLD.3.3)C0 / 5.19(ACJQ.4.4)C0 |
5.63(ACMU.3.4)C0 / 5.63(ACLD.3.4)C0 / 5.19(ACJQ.4.5)C0 |
| DSL/Ethernet CPE | EMG3525-T50B, EMG5523-T50B, VMG3625-T50B, VMG8623-T50B |
5.50(ABPM.9.11)C0 |
5.50(ABPM.9.12)C0 |
| DSL/Ethernet CPE | EX5601-T0, EX5601-T1 / EX5512-T0 / EX3600-T0 |
5.70(ACDZ.6.3)C0 / 5.70(ACEG.5.8)C0 / 5.70(ACIF.3.3)C0 |
5.70(ACDZ.6.4)C0 / 5.70(ACEG.5.9)C0 / 5.70(ACIF.3.4)C0 |
| DSL/Ethernet CPE | EX7501-B0 / EX7710-B0 / GM4100-B0 |
5.18(ACHN.3.4)C0 / 5.18(ACAK.1.9)C0 / 5.18(ACCL.2.2)C0 |
5.18(ACHN.3.5)C0 / 5.18(ACAK.1.10)C0 / 5.18(ACCL.3)C0 |
| Fiber ONTs | AM7510-00 / AX7501-B1 / PE5301-01 |
5.63(ACOR.0.4)C0 / 5.17(ABPC.8.1)C0 / 5.63(ACOJ.3.3)C0 |
5.63(ACOR.0.5)C0 / 5.17(ABPC.8.2)C0 / 5.63(ACOJ.3.4)C0 |
| Fiber ONTs | PM3100-T0, PM5100-T0, PM5100-T1 / PM7300-T0 / PM7500-00 |
5.42(ACBF.4.5)C0 / 5.42(ABYY.4.3)C0 / 5.61(ACKK.1.6)C0 |
5.42(ACBF.4.6)C0 / 5.42(ABYY.4.4)C0 / 5.61(ACKK.1.7)C0 |
Fiber ONT (CVE-2026-86676 only) |
PM5311-T0 |
1.00(ACFG.3)C0 |
1.00(ACFG.3.2)C0 |
| Wireless Extenders | WE3300-00 / WX3100-T0 / WX5600-T0 / WX5610-B0 |
5.70(ACKA.2.1)C0 / 5.50(ABVL.5.2)C0 / 5.70(ACEB.6.4)C0 / 5.18(ACGJ.0.6)C0 |
5.70(ACKA.2.2)C0 / 5.50(ABVL.5.3)C0 / 5.70(ACEB.6.5)C0 / 5.18(ACGJ.0.7)C0 |
Additional CVE-2026-79614 DSL/Ethernet models in Table 1 include EMG6726-B10A (5.13(ABNP.8.4)C0), EX2210-T0 (5.50(ACDI.2.8)C0), EX3500-T0/EX3501-T0 (5.44(ACHR.6.2)C0), EX3510-B0/B1 (5.17(ABUP.15.5)C0), EX5510-B0 (5.17(ABQX.11.4)C0), VMG3927-T50K/VMG4927-B50A (5.13(ABLY.10.4)C0), VMG4005-B50A/B60A (5.17(ABQA.3.6)C0), and VMG4005-B50B (5.13(ABRL.5.7)C0). Consult Zyxel's advisory for the exact model-by-model string before flashing.
Hardening & Remediation Playbook
Apply the following steps across branch-office gateways, ISP-managed CPE fleets, and home/SMB routers.
1. Inventory Hardware Models and Firmware Strings
Collect exact hardware model numbers and running firmware strings from all Zyxel CPE, ONT, and extender devices—including units deployed at remote worker sites or branch offices. Separate retail-managed units from ISP-leased units.
2. Obtain and Flash Patched Firmware
- Enterprise / Retail-Managed Hardware: Request the patched firmware file (
5.50(ABVY.8.4)C0or model-specific equivalent) from your Zyxel sales representative or support team, verify the file checksum, and schedule an immediate maintenance window to flash and reboot the device. - ISP-Supplied Hardware: Contact your ISP's support team to confirm whether they deploy custom-built firmware and when the November 17 patch will be pushed via TR-069/TR-369 auto-configuration servers (ACS).
3. Enforce Strict WAN and Guest-LAN Isolation
Verify that Remote Management (WAN HTTP/HTTPS) is disabled in the gateway's security/remote-management settings. On enterprise or multi-tenant networks, isolate the CPE/ONT management interface onto a dedicated management VLAN so untrusted LAN or guest Wi-Fi clients cannot reach libclinkc.so or the CGI admin portal.
4. Rotate Administrator Passwords and Audit Logs
Because CVE-2026-86676 can be triggered if administrator credentials are compromised, rotate device admin passwords to unique, high-entropy passphrases stored in a password manager, and check gateway syslogs for unexpected configuration changes, unknown admin logins, or anomalous outbound connections from the router itself:
# Example syslog audit on a central syslog collector receiving Zyxel CPE logs
grep -iE "login|httpd|cgi|admin|firmware|description" /var/log/remote-zyxel/*.log | tail -n 100
5. Rollback & Contingency Notes
Back up the device configuration (rom-0 / .conf backup) to an encrypted offline store before flashing firmware. If a newly flashed firmware build causes PPPoE, VoIP, or ISP VLAN incompatibilities, you can restore the saved configuration or coordinate with your ISP/Zyxel support representative before reverting—never leave an unpatched device exposed on WAN or untrusted LAN segments.
Frequently Asked Questions
Are Zyxel CPE and Fiber ONT devices exposed to CVE-2026-79614 over the internet by default?
No. Zyxel states that WAN access is disabled by default on the affected devices. However, if an administrator or ISP enabled remote WAN management—or if an attacker is already on the local LAN/Wi-Fi—the unauthenticated flaw is reachable.
Why aren't the firmware files listed as direct public downloads on the advisory? Zyxel's November 17, 2026 advisory states that these service-provider/CPE patches are distributed through Zyxel sales representatives or support teams, and ISP-supplied devices may require custom-built firmware directly from the ISP.
Does CVE-2026-86676 allow unauthenticated attacks?
No. CVE-2026-86676 is a post-authentication command injection flaw in the CGI Description parameter and requires administrator credentials. CVE-2026-79614 (libclinkc.so), however, is unauthenticated.
Is PM5311-T0 affected by CVE-2026-79614?
In Zyxel's November 17 advisory tables, PM5311-T0 (1.00(ACFG.3)C0, patched in 1.00(ACFG.3.2)C0) appears in Table 2 (CVE-2026-86676) and does not appear in Table 1 (CVE-2026-79614).
How do I check if my ISP-provided Zyxel router is patched? Log into the router's local admin status page to check the exact firmware version string, then contact your ISP's support team to confirm whether your build incorporates the November 17, 2026 fixes.
Sources
- Zyxel Networks — Zyxel security advisory for out-of-bounds write and post-authentication command injection vulnerabilities in certain DSL/Ethernet CPE, Fiber ONTs, and Wireless Extenders (Published November 17, 2026)
- Canadian Centre for Cyber Security — Zyxel security advisory (AV26-1167) (Published November 17, 2026)
- INCIBE-CERT — Múltiples vulnerabilidades en equipos de red de Zyxel (Published November 17, 2026)
- Tenable — CVE-2026-79614 and CVE-2026-86676 (November 17–18, 2026)
- Security.nl — Zyxel dicht beveiligingslekken in glasvezelmodems en wifi-extenders (Published November 17, 2026)